iSPIRT works to transform India into a hub for new generation software products, by addressing crucial government policy, creating market catalysts and grow the maturity of product entrepreneurs. Welcome to the Official Insights!
In July 2018, NITI Aayog published a Strategy and Approach document on the National Health Stack. The document underscored the need for Universal Health Coverage (UHC) and laid down the technology framework for implementing the Ayushman Bharat programme which is meant to provide UHC to the bottom 500 million of the country. While the Health Stack provides a technological backbone for delivering affordable healthcare to all Indians, we, at iSPIRT, believe that it has the potential to go beyond that and to completely transform the healthcare ecosystem in the country. We are indeed headed for a health leapfrog in India! Over the last few months, we have worked extensively to understand the current challenges in the industry as well as the role and design of individual components of the Health Stack. In this post, we elaborate on the leapfrog that will be enabled by blending this technology with care delivery.
What is the health leapfrog?
Healthcare delivery in India faces multiple challenges today. The doctor-patient ratio in the country is extremely poor, a problem that is further exacerbated by their skewed distribution. Insurance penetration remains low leading to out-of-pocket expenses of over 80% (something that is being addressed by the Ayushman Bharat program). Additionally, the current view on healthcare amongst citizens as well as policymakers is largely around curative care. Preventive care, which is equally important for the health of individuals, is generally overlooked.
The leapfrog we envision is that of public, precision healthcare. This means that not only would every citizen have access to affordable healthcare, but the care delivered would be holistic (as opposed to symptomatic) and preventive (and not just curative) in nature. This will require a complete redesign of operations, regulations and incentives – a transformation that, we believe, can be enabled by the Health Stack.
How will this leapfrog be enabled by the Health Stack?
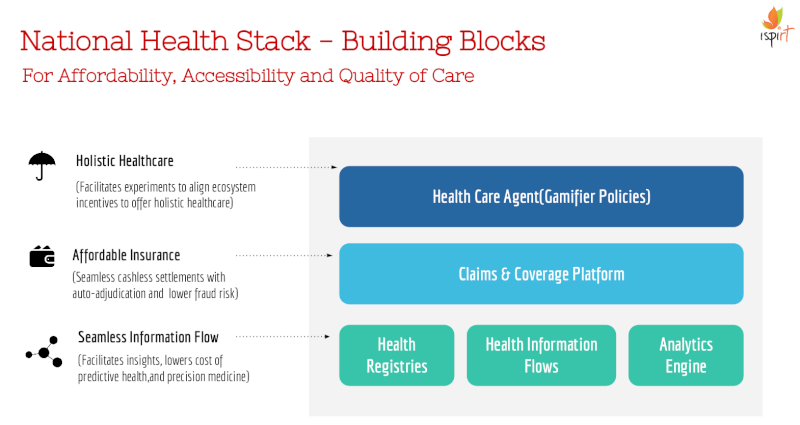
At the first level, the Health Stack will enable a seamless flow of information across all stakeholders in the ecosystem, which will help in enhancing trust and decision-making. For example, access to an individual’s claims history helps in better claims management, a patient’s longitudinal health record aids clinical decision-making while information about disease incidence enables better policymaking. This is the role of some of the fundamental Health Stack components, namely, the health registries, personal health records (PHR) and the analytics framework. Of course, it is essential to maintain strict data security and privacy boundaries, which is already considered in the design of the stack, through features like non-repudiable audit logs and electronic consent.
At the second level, the Health Stack will improve cost efficiency of healthcare. For out-of-pocket expenditures to come down, we have to enable healthcare financing (via insurance or assurance schemes) to become more efficient and in particular, the costs of health claims management to reduce. The main costs around claims management relate to eligibility determination, claims processing and fraud detection. An open source coverage and claims platform, a key component of the Health Stack, is meant to deal with these inefficiencies. This component will not only bring down the cost of processing a claim but along with increased access to information about an individual’s health and claims history (level 1), will also enable the creation of personalised, sachet-sized insurance policies.
At the final level, the Health Stack will leverage information and cost efficiencies to make care delivery more holistic in nature. For this, we need a policy engine that creates care policies that are not only personalized in nature but that also incentivize good healthcare practices amongst consumers and providers. We have coined a new term for such policies – “gamifier” policies – since they will be used to gamify health decision-making amongst different stakeholders.
Gamifier policies, if implemented well, can have a transformative impact on the healthcare landscape of the country. We present our first proposal on the design of gamifier policies, We suggest the use of techniques from microeconomics to manage incentives for care providers, and those from behavioural economics to incentivise consumers. We also give examples of policies created by combining different techniques.
The success of the policy engine rests on real-world experiments around policies and in the document we lay down the contours of an experimentation framework for driving these experiments. The role of the regulator will be key in implementing this experimentation framework: in standardizing the policy language, in auditing policies and in ensuring the privacy-preserving exchange of data derived from different policy experiments. Creating the framework is an extensive exercise and requires engagement with economists as well as computer scientists. We invite people with expertise in either of these areas to join us on this journey and help us sharpen our thinking around it.
Do you wish to volunteer?
Please read our volunteer handbook and fill out this Google form if you’re interested in joining us in our effort to develop the design of Health Stack further and to take us closer to the goal of achieving universal and holistic healthcare in India!
This PolicyHacks recording was done on 2nd January 2018 at 5.30 pm covering a discussion on the proposed rules ( amendment ).
iSPIRT Volunteers, Sanjay Jain, Saranya Gopinath, Venkatesh Hariharan (Venky), Tanuj Bhojwani iSPIRT volunteers and Bhusan, a lawyer from IDFC participated in the discussions with Sudhir Singh.
The main aspects of the draft amendment and its impact on the Software product and Start-ups in tech world in India are covered in the discussions. A transcript of the discussion is given below for read. Or you could choose to listen to the recorded audio/video on you tube embedded below.
The draft rules mainly cover information published by users on intermediaries also referred to as platforms in this discussion. The three broad aspects that draft rules cover are :
Putting higher onus on Intermediaries on objectionable content
High level of compliance and penalties
Enforcing traceability of objectionable content
With above introduction to topic floor was opened for discussions by host Sudhir Singh. Below is the transcript of contribution made by participants ( the transcript may not be complete word by word but follows the semantics of contribution made).
On Question on how the draft rules will impact industry
Sanjay Jain – “Two three element that you have highlighted in there.
First is the definition of the platform player. Intermediaries are broadly defined. They include everybody from telecom players, ISPs, a Social network and even a site like apartment Adda, Baba-jobs, because all of these will have some kind of user generated content, which is being published and shared with others. While the law drafting may have had one type of intermediary in mind, but it actually applies to all of them and as such that is where some of the issue starts.
Second part is that by moving some of the Onus to the platform, and I actually think they have not fully moved the onus to the platform, which is very dicey situation because, they have moved and not moved at the same time. And because, the onus is primarily still on the Govt. to notify to the intermediary, that there is something objectionable and they have to remove it. But, at the same time they have said that intermediary shall develop technological means for identifying all of this, as well. Sometimes there is an assumption that technology can do a lot, and in reality while you can have 99.9% accuracy, you still have those 0.1% and that becomes an issue.
Third part, I wanted to say is cost of compliance goes up considerably. They have put a limit 50 Lakh users in India, though we believe 50 lakh may either be little low. They should go little higher and depending upon type of user generated content they should allow for little graded form of compliance.”
Bhusan, from IDFC Institute – “As a context, these rules have come about are drafted based on earlier rules of 2011 and have some new features like graded approach such as significant intermediary to non-significant intermediary. They have put time lines in terms of response from intermediary and so these rules are being built upon existing set of rules.
There is some short of tightening of the compliance on intermediary e.g. 72 hours of time line for response. If you are a significant intermediary, than you have to be incorporated in India and has to appoint a person who is available 24X7, and you also have to have proactive measure to screen content on your side. Some of this is coming from frustration of getting information from intermediaries.”
On issue of how much these numbers are practical for small players? How to save start-ups?
Sanjay Jain – “Differed assumption is that if you publish any content which is against the law, you are liable. Being an intermediary protects you. If you remember the case of Baje.com, the only protection they got was proving to be an intermediary. Hence, you want to call them (Start-ups) intermediaries but get a better procedural control to stop harassment at hand of low level law enforcement.”
Tanuj came in and quoted the the line after 72 hours, in section 5 it says”as asked for by any government agency or assistance concerning security of the State or cyber security; or investigation or detection or prosecution or prevention of offence(s); protective or cyber security and matters connected with or incidental thereto.”
According to Tarun, this statement is so broad that any junior level officer can say I got information that someone from Hissar in Haryana is harassing a person and give information of all users in Haryana.
Venky – “I agree with Tarun, we have the laws or the rule meant to be more sharply defined and have sharp implementation guidelines. In this case seems to be pretty loosely framed.”
Sudhir Singh – “There is another issue in draft rules on once in a month information to user, and taking their consent. Any hard compliance of rules is normally easier for large players, they may easily invest and handle with technology but small players and start-ups it is difficult situation to comply.”
Sanjay – “From technology experience we learn that if you make something automated, user ignore it. So, what will happen is this will be implemented by sending one email to every user, once in a month, stating if you don’t comply, we will delete your account from platform.
That’s an email that is going to get ignored. So, it is a very ineffective suggestion. Also, there is an implicit assumption that all users are identifiable, which is not the case always. So, just to implement it you will have to identify users. That may not be a valid requirement.”
Bhusan – “On the point that you need to have more than 5 million users. My question is procedurally how do you even establish that?
Will platform will have to do GPS type of tracking to ensure that and does this not create a privacy risk in itself e.g. I do not know does platforms like Quora know that they have more than 5 million users in India or not. It seems, there is this focus on regulating Big Techs and this 5 Million number really come from that.”
Sanjay – “Basically, anybody can be hosting user generated content. So, lets us say we are on a common platform, and there is a message flowing from me to you. If I violate the law, and let’s say the message is liable of incitement or any other law, then I should be held liable and not the platform.
For that platform needs to be qualified as intermediary, put under safe harbour and intermediary takes on the responsibility of helping the law enforcement. So, we should not take up start-ups out of its ambit. What we have to do is make sure that, the conditions required is that conformance to the standard should not be so terrible that start-up should be excluded.
So, we need to sharpen the requirement they they should be conforming with and make it easy enough for somebody to confirm.”
It is being discussed that Govt. is aiming for higher level of Penalty. What should be our recommendation?
Tanuj – “If you take very young company any short of hit is bad, but if you can put proportion of revenue basis, it will be at least more forward thinking, even if it is not absolutely fair, in some sense more fair of not having that rule or having flat rule. The amendments of changes we should think about of moving the penalty would be not being in favour of arbitrary penalty.”
Tarun added – “Our recommendations should be around sharpening rules, like who can use it who cannot use, what are the accountability measures on them, more than magnitude of these numbers.”
Saranya – “Just to address the Data protection law vis-à-vis intermediary act. The subject matter of Data Protection law is ‘personally identifiable information’, whereas Intermediary act tries to cover ‘all communication in some sense’ and hence, Intermediary act has a longer leash with regard to the person who can take the intermediaries to task.
The criteria of what would be offensive under Intermediary act is very different e.g. encouraging consumption of narcotics. Hence, the criteria that a person can take intermediary to task is extremely wide and needs to be curtailed.”
Bhusan – “There is an inherent subjectivity in these rules and there is need to some short of standard procedures on how these rules are applied by law enforcement agencies across. All that these rules say is – any request has to come in writing and intermediaries have to comply with.”
Venky – “From an implementation perspective we need implementation guideline. Section 5 is so wide that anybody can drive a truck through it.”
How the numbers (e.g. 72 hours period to respond and 50 lakh users) should be defined in a manner that is suits Start-ups who are in the early phase.
Sanjay – “Broadly, we need to identify the places and various numbers to apply proportionally depending upon the size of entity and size of violation, in our feed back to the Government.”
Sanjay also brought in attention to the “Appropriate Govt”, needs to be defined well. He said, “What we want is the Govt. agencies to be defined.”
Bhusan – “This is very standard way of defining. I have not seen any precise definition on specifying agencies in general regulation and I do not see they will start with IT act on this.
Bhusan mentioned another important issue of end-to-end encryption is a more political point rather than national security issue. (refer section 5 last lines).
Sanjay – “This is about tracking and tracing may not be about encryption. The fact, that I sent information to some body is about meta data, it’s not about information itself. This may be clarified better, but is not about end-to-end encryption but about meta data.”
Sanjay further added, “perhaps one clause you could add is to say that the ‘intermediary should be able to do this based on the information it has, if it does not have information, there should be not requirement to maintain information’ e.g. if you take business of mailinator, they don’t keep record of mails sent in and out.”
Bhusan, added “it should not lead to intermediaries having a requirement to do KYC on users.”
Is 50 lakh only to target large platform players?
Sanjay, “my read is they may have thought that way. But in reality a regional ISP or even a small newspaper will fall in to that category.”
“Bhusan, I don’t think it is a number generate by some study, but it seems like they just picked it.”
The discussion was rapped with thanks to all players.
Author note and Disclaimer:
PolicyHacks, and publications thereunder, are intended to provide a very basic understanding of legal/policy issues that impact Software Product Industry and the startups in the eco-system. PolicyHacks, therefore, do not necessarily set out views of subject matter experts, and should under no circumstances be substituted for legal advice, which, of course, requires a detailed analysis of the relevant fact situation and applicable laws by experts in the subject matter on case to case basis.
PolicyHacks discussions and recordings are intended at issues concerning the industry practitioners. Hence, views expressed here are not the final formal official statement of either iSPIRT Foundation or any other organisations where the participants in these discussions are involved. Media professionals are advised to please seek organization views through a formal communication to authorised persons.
“High share premium is not the basis of a high valuation but the outcome of valid business decisions. This new whitepaper by our iSPIRT policy experts highlights how share premia is a consequence of valid business decisions, why 56(2)(viib) is only for unaccounted funds and measures to prevent valid companies from being aggrieved by it”
Drones have been around for a long time, going back as far as World War II. For most of their history, they were considered part of the military arsenal and developed and deployed almost exclusively by the military.
However, the past decade has seen a tremendous amount of research and development in the area of using drones for civilian purposes. This has led industry experts to predict that drones will be disrupting some of the mainstay industries of the global economy such as logistics, transportation, mining, construction and agriculture to name a few. Analysts estimate a $100 billion market opportunity for drones in the coming few years[1]. In spite of the overwhelming evidence in favour of the value created by drones, it has taken quite a few years for the drone industry to take off in a commercial sense globally.
The main reason for this has been the regulatory challenges around what is allowed to fly in the air and where is it allowed to fly. A common theme around the world is the unconventional challenges that old governmental structures have to face as they try to understand and regulate new technologies. Hence the default approach so far for governments has been reactionary caution as they try to control what are, essentially, flying robots in the sky.
However, with electronic costs coming down, the hardware becoming more accessible and the software interpreting data becomes more powerful a number of humanitarian, civilian and industrial application have emerged and as governments across the world are realizing the potential of drones, we are starting to see the first version of regulations being drafted and adopted across the globe.[2]
Closer home India has a relatively adverse approach to drones or more lackadaisical rather. [3]
But as India continues to drive to become a more technology-oriented economy the role of drones in the worlds fastest growing economy and the potential benefits it can bring are hard to ignore.[4]
However, India’s approach to drone regulations cannot be that of other major economies that have the luxury of friendly neighbours and a large network of monitoring apparatus, India has had to take an approach that has to be novel and robust. Something that balances the security landscape while also being designed to allow maximum utilization of the potential that drones offer. Out of this need to both regulate secure how and where a drone can fly and keep multi-ministerial stakeholder interests accounted for was born the Digital Sky, India’s foundational framework for all things drones.
What is the Digital Sky and how does it work?
What the Digital Sky accomplishes beautifully is to fill the institutional void that needs to be collectively fulfilled by so many institutions and make it easier for the industry and consumers to interface with the government legally through one platform. Permission to fly drone no longer requires a 90-day intimation with an arbitrary number of NOCs to be approved by umpteen number of ministerial bodies at the central and federal level. The industry and the public now know one place to interact with in order to register their drone, get recognised as a certified operator and apply for permissions and all concerned government agencies ensure their overarching interests do not interfere with the large-scale adoption of drones.
There are crucial components required for the Digital Sky concept to work, the most central being that drone operators should not be able to fly drones if they are not approved by the government. To accomplish this the Drone 1.0 regulations revolve around the concept of No-Permission-No-Takeoff (NPNT).
Our maven Tanuj Bhojwani explaining NPNT at the DigitalSky RoundTable on 4 Dec 2018 in Bengaluru
What this implies is that unless a drone has got valid permission for a particular flight through tamper-proof digitally signed permission tokens, it will not be able to take off. The Digital Sky is the platform to automate the processing of these permission tokens as they flow in from different parts of the country without overwhelming the authorities through a flight information management system (one of only three countries to build this nationally after China and the USA). In order for this vision to come true, there will be an enormous change in the way drones are manufactured and operated. Entire new industry verticals around getting existing drones compliant, developing interfaces that interact with the Digital Sky platform and making applications for India’s needs will develop. Hence this begs the question.
How are the current state of the industry are changing with 1.0 regulations
Until the introduction of the regulations companies especially in the UAV operations were doing non-restricted work and end up becoming the jack-of-all-trades. Companies in the manufacturing domain were unclear of who is their target customer and what they needed to build. All the companies in this domain were working with no clarity on the safety and permissions.
With the introduction of the Drone Policy 1.0, there is a buzz which has been created and efforts are being made to understand the regulations by all the entities who are set to gain from it. They understand that there will be a new aspect that needs to cater to i.e. the sense of accountability.
For manufacturer’s The NP-NT mandate will be the most immediate requirement, the most common route to implement the mandate will be through changes to existing firmware architecture. The changes themselves are being driven by open source initiatives with various operators, system integrators and manufacturers contributing to the shift to NP-NT for all major drone platforms in the country. The Digital Sky has inadvertently catalysed the first industry-wide initiative to bring together all members of the ecosystem. Other requirements such as ETA bring in much-needed standardisation in the hardware space, this allows benchmarking of products, easier availability of information about the standards to look out for end users.
For operators, a massive increase in the volume of business is expected as they can now focus on getting certified drones into the air, and not so much on getting approvals. The Digital Sky brings in much-needed certainty and predictability into an industry that will be focused on balancing demand and supply of drone-related operations in a market that has a huge need for drones and their data but limited expertise to acquire and process it. This also puts onus an industry to become security and privacy conscious and insurance agencies will play an important role in this regard. It will also immensely help in changing the thought process of the companies providing services and their customers. Customers will start understanding that they also need to have a defined plan, process and execution instead of a haphazard existing process of execution.
How industry/playground will change over the coming years?
With the introduction on the regulations and a platform like Digital sky enabling the ease of doing business for the companies who are serious stakeholders in this domain, there is no limit to what developments will occur in the coming years. It opens up possibilities for utilization of Drone and its related technologies in Agriculture, Medical, Energy and Infrastructure and transportation.
The existing players will become more mature and more focused. They will understand that with regulations in place a more focused approach is the key to scale. They will look at opportunities to compete with the global market also as the solutions that are developed around the Drone Regulations 1.0 and 2.0 will be key factors that contribute to the Indian ecosystem to becoming a global standard to test, adapt and innovate drone applications and management.
What are the opportunities? What does that mean for the current and new players?
UAV/ Drones as a business was a far-fetched thought for many entrepreneurs and has been a struggling industry in the past in India. Going forward it is guaranteed that it will be one of the biggest markets in the world for UAV as a business. What the regulations and Digital Sky platform will enable is a new levelled playground ground for the UAV companies to initiate good scalable business models both existing and the ones entering new to the sector.
The existing companies with the right resources can now plan to scale their operations and also have the added advantage of doing work for the private sector in India. Due to the restrictive method of operations adapted previously the solutions to private agencies was unavailable. Now going forward the companies will shift their focus from being a B2G entity to a B2B entity. Many new businesses for UAV air traffic management, surveillance, AI and ML-based UAV solutions and deliveries will emerge out of India with technology specific to India.
In 2016, the company I co-founded, Thinkflow, went through a liquidity event. It was a great outcome for all and I was thinking of the next move. It was natural for me to think of starting again. I was wiser, had seed capital and only had to find a problem attractive enough. It looked like I was going down that path and would build another software product company for the global market. Something interesting was happening in India at that same time. All the global giants were investing in or had invested in companies that were building for India. Venture funds like Softbank, DST Global, Naspers were making bold bets in the Indian consumer space. A lot of digitization was also happening in India. UPI was in the initial release phase (Flipkart had already committed to back PhonePe, when it was just Sameer and Rahul’s idea), the GST bill was tabled in Parliament, a system to track real-time movement of goods was being discussed. It was really a lot of action and if venture investments were any indication, it was the validation of the India story. In a meeting with Sharad, for the first time, I understood the true potential of the digital stack (now called the IndiaStack) that was taking shape then. While the stack was not fully ready for all the use cases that we covered in the meeting, the vision to solve some of the hardest problems India was facing through technology was fascinating. That vision combined with the kind of commitment the Open API team (it is now called the IndiaStack team) put in is unparalleled in my experience I left the meeting with a question from Sharad. “Do you want to do a 2-year MBA that pays you a small stipend?”. I thought about it and said ‘yes’. Amongst all the challenges, unlocking credit for small businesses resonated with me. Having faced the consequences of not having access to timely credit during my Thinkflow days, I could identify with this problem and ended up doing work around data-driven and cash-flow lending. We make a number of decisions in a lifetime but a few handfuls of them are life-changing. And my decision to work with iSPIRT and to focus on Flow-based lending has been a life-changing one. Over the last 30 months, I worked towards Improving efficiencies in the loan delivery and collections cycle so we could bring a lot more borrowers to the formal system. As an iSPIRTer, I had the privilege of working with CEOs of banks, NBFCs and Small Finance banks to design new loan products. We were working on new ways to use data to underwrite small loans for new-to-credit businesses. I was guiding them on how to use technology to deliver credit at lower costs and worked alongside them to devise new strategies to build new workflows around origination, disbursement, collections, et al. The iSPIRT stint has been a rewarding one. iSPIRT is all about putting country first and solving country scale problems. Core values such as this and others like setting up fellow volunteers for success were totally unheard of to me in the modern day workplace. iSPIRT is a safe space for any volunteer who is passionate about changing India. The institution has been about investing in the success of its fellows – I had the benefit of learning from the wisdom of people like Nandan Nilekani, Sharad Sharma, Pramod Varma, Sanjay Jain. My colleagues are A-players and I had the opportunity to learn from and work alongside Meghana Reddyreddy, Nikhil Kumar, Venkatesh Hariharan, Jai Shankar, Tanuj Bhojwani, Siddharth Shetty and Karthik As I prepare to roll-off my responsibilities at iSPIRT, I want to express my gratitude and a special thanks to Sharad Sharma for giving me this opportunity. He is a great guide and has been a great mentor for me. Thank you for being there for me when I needed you. It has been a great experience working with you and the team and my learnings here are my core strength as I move on to solving for India through my next venture.
iSPIRT has been actively engaged in pursuing the favourable policy for the Cloud Telephony sector in Telecom Industry, an amalgamation of the various IT and Communications technologies.
National Digital Communication Policy has been announced recently and it is encouraging to see the announcements in the policy on some common issues to do with Startup ecosystem and digital communication aspects of the Cloud Telephony Players.
We are expecting the Department of Telecom (DOT) to further work on implementation and framing of rules and regulation in light of policy in near future. Despite many positive directional changes, there is a need to develop a regulatory framework for the Cloud Telephony players. Cloud Telephony players are adding value to communication and hence to the economy in several innovative ways. In addition, they also add a good revenue stream to licenses Telecom Service Providers (TSPs).
This PolicyHacks session is devoted to the critical analysis of the NDCP for this sub-sectoral player. Some of the entrepreneurs involved in the discussion are Gurumurthy Konduri of Ozonetel, Ujwal Makhija of PhoneOn, Gaurav Agrawal of Exotel and Gaurav Sawhney of Knowlarity.
A recording of this discussion is given below. Please feel free to click and watch. (About 20 seconds lost in the opening frame, apologises for the error)
The main point covered in the discussion is summed up below as are the some of our recommendations and good work is done (while the Policy was in the draft stage and during various consultation processes), which have been reflected in the policy under respective sections as under:
Page 7
1.1.(f) – Encourage and facilitate sharing of active infrastructure by enhancing the scope of Infrastructure Providers (IP) and promoting and incentivising the deployment of common sharable, passive as well as active, infrastructure
1.1.(g).iv. – Allowing benefits of convergence in areas such as IP-PSTN switching.
Both of these are encouraging moves however it is to be seen how further rules and framework make easy for Small and Startup companies to use them without licensed TSPs creating a barrier for them.
Page 8
1.1.(j) – By encouraging innovative approaches to infrastructure creation and access including through resale and Virtual Network Operators (VNO)
This is a very encouraging announcement for the Cloud Telephony startups.
Page 14
2.1. (c ) iv. – Improving the Terms and Conditions for ‘Other Service Providers’, including definitions, compliance requirements and restrictions on inter-connectivity
2.1.(c ).viii. – Creating a regime for fixed number portability to facilitate one nation – one number including portability of toll-free number, Universal Access numbers and DID numbers
Again very encouraging but needs some boost up. Audiotex regime must go most speakers feel and all the players in Cloud telephony are treated as ASP. These provisions will help cloud telephony to deliver better value propositions in their offerings.
Page 15
2.2.(a) iv: – Encourage use of Open APIs for emerging technologies
2.2. (b) – Promoting innovation in the creation of Communication services and network infrastructure by Developing a policy framework for ‘Over The Top’ (OTT) services.
2.2.(f) ii. – Enabling a light touch regulation for the proliferation of cloud-based systems
2.2.(f).iii. – Facilitating Cloud Service Providers to establish captive fibre networks.
A welcome move to encourage Open APIs. However, licenses TSP should be given one standard that is governed by DOT to implement any APIs that let them monitor cloud telephony or ASPs on their network, instead of allowing them to create a regime of their own.
Generally, an OTT policy is recommended in reforming the sector. However, OTT framework should not be mixed with ASP or Cloud Telephony providers. It is better to keep a distinction between the two.
Page 17:
2.4.(a).ii: – Promoting participation of Start-ups and SMEs in government procurement
2.4.(b). – Reducing the entry barriers for start-ups by reducing the initial cost and compliance burden, especially for new and innovative segments and services.
Acceptance of these issues is very encouraging. The Government can be a very big user of the Cloud Telephony industry also. And we hope this will turn out to be a winning proposition for the Cloud Telephony industry in near future.
Conclusion
Whereas this policy announcement reflects a positive change, it is yet to be seen how DOT look at Cloud Telephony and provides it with a recognition as a sub-sector with easy and proper regulatory framework for same.
Note: The above article is co-authored by Gurumurthy Konduri of Ozonetel with Sudhir Singh of iSPIRT
One would think that the new sexy in the startup capital of the world is self-driving cars, AI/ML… I got news for you! AI/ML (esp. Machine Learning) is not listed in Gartner’s hype cycle for 2018.
This was corroborated on my recent trip to the valley and the US east coast, where I met several investors, founders, corp dev and other partners of the startup community. It was evident that the AI/ML hype which peaked in 2016 & 2017 is no longer considered a buzzword. It is assumed to be table stakes. What you do with AI/ML is something everyone is willing to listen to. Using AI/ML to solve a high-value B2B SaaS problem is Sexy! (Gartner trends for 2018).
As the hype with AI/ML settles down, B2B startups across the globe are discovering the realities of working the AI/ML shifts for SaaS. Many AI tools & frameworks in the tech stack are still evolving and early pioneers are discovering constraints in the stack and creatively building workarounds as they build their products.
Many entrepreneurs are watching from the sidelines the unfolding of the AI/ML hype, wondering on many valid questions like these (and more):
Q: Do I have to stop what we are building and jump onto the AI bandwagon? No. Q: Are the AI/ML resources mature & stable to build better value products? No, they are still evolving. Q: Do I need expensive investments in constrained resources? No, not until you have a high-value problem to solve.
B2B SaaS startups go through 2 key struggles. How to find market-fit and survive? And how to stay relevant and grow. And if you don’t evolve or reinvent as the market factors change, there are high chances for an upstart to come by and disrupt you. The iSPIRT entrepreneur playbooks look to help entrepreneurs get clarity on such queries and more. Our goal is to help our startups navigate such market shifts, stay relevant and grow. Our mini roundtables Playing with AI/ML are focused on WhyAI for SaaS discussions in multiple cities. If you or a startup you know may benefit do register
The MiniRT Agenda
Seeding & creating an active discussion on Why AI/ML? What is the higher order value being created? How to identify the value & opportunities to leverage AI? How to get started with an AI playground (if not already running)? How to think of data needs for AI/ML investments, How to address the impact on Product & Business… Insights from these sessions are meant to help refine our approach & readiness to leverage AI/ML for building higher order value products. And in doing so building a vibrant community focused around navigating this shift.
Upcoming PlaybookRTs on AI/ML
6-Oct (Chennai) 10 am – 1 pm – MiniRoundTable on WhyAI for B2B SaaS – Shrikanth Jagannathan, PipeCandy Inc 18-Oct (Bangalore) 6 pm – 8 pm – MiniRoundTable with Dr Viral Shah on AI/ML Tools & discuss your ML/DeepLearning challenges 27-Oct (Delhi/Gurgaon) 2 pm – 6 pm – MiniRoundTable on WhyAI for B2B SaaS, Adarsh Natarajan, CEO & Founder – Aindra Systems TBD (Bangalore) – MiniRoundTable on WhyAI for B2B SaaS, (based on registered interest) TBD (Mumbai) – MiniRoundTable on WhyAI for B2B SaaS, (based on registered interest)
The AI+SaaS game has just begun and it is the right time for our hungry entrepreneurs to Aspire for the Gold, on a reasonable level playing field.
Please note: All iSPIRT playbooks are pro-bono, closed room, founder-level, invite-only sessions. The only thing we require is a strong commitment to attend all sessions completely and to come prepared, to be open to learning & unlearning, and to share your context within a trusted environment. All key learnings are public goods & the sessions are governed by the Chatham House Rule.
On behalf of iSPIRT, Sanjay Jain recently published an opinion piece regarding the recent supreme court judgement on the validity of Aadhaar. In there, we stated that section 57 had been struck down, but that should still allow some usage of Aadhaar by the private sector. iSPIRT received feedback that this reading may have been incorrect and that private sector usage would not be allowed, even on a voluntary basis. So, we dug deeper, and analyzed the judgement once again, this time trying to disprove Sanjay’s earlier statement. So, here is an update:
Section 57 of the Aadhaar act has NOT been struck down!
Given the length of the judgement, our first reading – much like everyone else’s was driven by the judge’s statement and confirmed by quickly parsing the lengthy judgement. But in this careful reanalysis, we reread the majority judgement at leisure and drilled down into the language of the operative parts around Section 57. Where ambiguities still remain, we relied on the discussions leading up to the operative conclusions. Further, to recheck our conclusions, we look at some of the other operative clauses not related to Section 57. We tested our inference against everything else that has been said and we looked for inconsistencies in our reasoning. Having done this, we are confident in our assertion that the judges did not mean to completely blockade the use of Aadhaar by private parties, but merely enforce better guardrails for the protection of user privacy. Let’s begin!
Revisiting Section 57
Here is the original text of section 57 of the Aadhaar Act
Nothing contained in this Act shall prevent the use of Aadhaar number for establishing the identity of an individual for any purposea purpose backed by law, whether by the State or any body corporate or person, pursuant to any law, for the time being in force, or any contract to this effect:
Provided that the use of Aadhaar number under this section shall be subject to the procedure and obligations under section 8 and Chapter VI.
Now, let us simply read through the operating part of the order with reference to Section 57, ie. on page 560. This is a part of paragraph 447 (4) (h). The judges broke this into 3 sections, and mandated changes:
‘for any purpose’ to be read down to a purpose backed by law.
‘any contract’ is not permissible.
‘any body corporate or person’ – this part is struck down.
Applying these changes to the section, we get:
Nothing contained in this Act shall prevent the use of Aadhaar number for establishing the identity of an individual for any purposea purpose backed by law, whether by the State or any body corporate or person, pursuant to any law, for the time being in force, or any contract to this effect:
Provided that the use of Aadhaar number under this section shall be subject to the procedure and obligations under section 8 and Chapter VI.
Cleaning this up, we get:
Nothing contained in this Act shall prevent the use of Aadhaar number for establishing the identity of an individual pursuant to any law, for the time being in force:
Provided that the use of Aadhaar number under this section shall be subject to the procedure and obligations under section 8 and Chapter VI.
It is our opinion that this judgement does not completely invalidate the use of Aadhaar by private players, but rather, specifically strikes down the use for “any purpose [..] by any body corporate or person [..] (under force of) any contract”. That is, it requires the use of Aadhaar be purpose-limited, legally-backed (to give user rights & protections over their data) and privacy-protecting. As an exercise, we took the most conservative interpretation – “all private use is struck down in any form whatsoever” – and reread the entire judgement to look for clues that support this conservative view.
Instead, we found that such an extreme view is inconsistent with multiple other statements made by the judges. As an example, earlier discussions of Section 57 in the order (paragraphs 355 to 367). The conclusion there – paragraph 367 states:
The respondents may be right in their explanation that it is only an enabling provision which entitles Aadhaar number holder to take the help of Aadhaar for the purpose of establishing his/her identity. If such a person voluntary wants to offer Aadhaar card as a proof of his/her identity, there may not be a problem.
Some pointed out that this is simply a discussion and not an operative clause of the judgement. But even in the operative clauses where the linking of Aadhaar numbers with bank accounts and telecom companies is discussed, no reference was made to Section 57 and the use of Aadhaar by private banks and telcos.
The court could have simply struck down the linking specifically because most banks and telcos are private companies. Instead, they applied their mind to the orders which directed the linking as mandatory. This further points to the idea that the court does not rule out the use of Aadhaar by private players, it simply provides stricter specifications on when and how to use it.
What private players should do today
In our previous post, we had advised private companies to relook at their use of Aadhaar, and ensure that they provide choice to all users, so that they can use an appropriate identity, and also build in better exception handling procedures for all kinds of failures (including biometric failures).
Now, in addition to our previous advice, we would like to expand the advice to ask that each company look at how their specific use case draws from the respective acts, rules, regulations and procedural guidelines to ensure that these meet the tests used by this judgement. That is, they contain adequate justification and sufficient protections for the privacy of their users.
For instance, banks have been using Aadhaar eKyc to open a bank account, Aadhaar authentication to allow operation of the bank accounts, and using the Aadhaar number as a payment address to receive DBT benefits. Each of these will have to be looked at how they derive from the RBI Act and the regulations that enable these use cases.
These reviews will benefit from the following paragraphs in the judgement.
The judgement confirmed that the data collected by Aadhaar is minimal and is required to establish one’s identity.
Paragraph 193 (and repeated in other paras):
Demographic information, both mandatory and optional, and photographs does not raise a reasonable expectation of privacy under Article 21 unless under special circumstances such as juveniles in conflict of law or a rape victim’s identity. Today, all global ID cards contain photographs for identification alongwith address, date of birth, gender etc. The demographic information is readily provided by individuals globally for disclosing identity while relating with others and while seeking benefits whether provided by government or by private entities, be it registration for citizenship, elections, passports, marriage or enrolment in educational institutions …
The judgement has a lot to say in terms of what the privacy tests should be, but we would like to highlight two of those paragraphs here.
Paragraph 260:
Before we proceed to analyse the respective submissions, it has also to be kept in mind that all matters pertaining to an individual do not qualify as being an inherent part of right to privacy. Only those matters over which there would be a reasonable expectation of privacy are protected by Article 21…
Paragraph 289:
‘Reasonable Expectation’ involves two aspects. First, the individual or individuals claiming a right to privacy must establish that their claim involves a concern about some harm likely to be inflicted upon them on account of the alleged act. This concern ‘should be real and not imaginary or speculative’. Secondly, ‘the concern should not be flimsy or trivial’. It should be a reasonable concern…
Hence, the privacy risk in these use cases must be evaluated in terms of the data in the use case itself, as well as in relation to biometrics, and the Aadhaar number in the context of the user’s expectations, and real risks. Businesses must evaluate their products, and services – particularly those which use Aadhaar for privacy risks. It is helpful that the UIDAI has provided multiple means of mitigating risks, in the form of Registered Devices, Virtual Ids, Tokenization, QR Codes on eAadhaar, etc. which must be used for this purpose.
What private players should do tomorrow
In the future, the data protection bill will require a data protection impact assessment before deploying large scale systems. It is useful for businesses to bring in privacy and data protection assessments early in their development processes since it will help them better protect their users, and reduce potential liability.
This is a useful model, and we would hope that, in light of the Supreme Court judgement, the Government will introduce a similar privacy impact review, and provide a mechanism to regulate the use of Aadhaar for those use cases, where there are adequate controls to protect the privacy of the users and to prevent privacy harms. Use cases, and an audit/enforcement mechanism matter more than whether the entity is the state, a public sector organization, or a private sector organization.
Note: This is in continuation of Sanjay Jain’s previous op-ed in the Economic Times which is available here and same version on the iSPIRT blog here.
The writer is currently Partner, Bharat Innovation Fund, and Chief Innovation Officer at the Centre for Innovation, Incubation and Entrepreneurship, IIM Ahmedabad. As a volunteer at iSPIRT, he helped define many of the APIs of the India Stack. He was the Chief Product Manager of UIDAI till 2012
Data protection and privacy have been a topic of hot debates and discussion in recent times in India. It had become extremely important as India is progressing to a be a “Digital economy” to address this issues relating to the use of personal data.
iSPIRT has been in forefront of developing Consent Framework and called as Data Protection & Empowerment Architecture (DEPA). The Account Aggregator Policy of RBI revolves around this consent architecture.
Whereas the bill is of interest to almost all the sectors of the economy, it is extremely important for businesses in Information Technology sector and especially in Software product Industry to understand the law as it is seeded and further as it evolves.
The bill has many aspects to it in the legal framework. It is not possible to cover the entire understanding of the bill in one blog. We have attempted to cover some salient features that may be important for the Software Product Industry as well as how it contacts with the techno-legal aspects of DEPA as it stands in financial sector, perhaps to be replicated in other important sectors of the economy.
This blog is again posted in a Question and answer format both as a video and as a transcript of the video. You can use the one you like.
Questions have been asked by iSPIRT volunteer and Policy expert Mr Sudhir Singh and answered by Supratim Chakraborty (Data Privacy and Protection expert from Khaitan & Co.) and Siddharth Shetty (leading the DEPA initiative at iSPIRT).
What are the most important aspects of the bill?
Supratim answered, “What we have seen is through this draft bill, there is an attempt to establish the relationship of trust between the data subject and data controller. The nomenclature has been changed in this bill and It is data fiduciary and data principles. It puts a lot of onus on the data fiduciary to take care of data care protection.”
“There are several important aspects of the bill that needs attention such as localisation of data, cross-border transfer and also some other aspects such as privacy by design, transparency requirement, security safeguard, breach notification, grievance redressal mechanism, the requirement of Data protection officer, record keeping requirements”, as elaborated Supratim.
Is there some restriction on data fiduciary? Is the state exempted?
Supratim said, “this bill is equally applicable to private parties and the Government unlike earlier provisions of section 43A and 72A of IT ACT. 43A will be scrapped after this bill comes into existence. There has been a lot of debate on this aspect of bringing Govt. under the purview of the law.”
Is right to be forgotten covered in a similar way as GDPR?
Supratim explained, “Our Govt. has looked at this in a more business-friendly way by covering the right to be forgotten by provisioning that any further dissemination of data should be stopped, once the data principal chooses to withdraw the consent or ask for the right to be forgotten.”
He described four governing aspect that explains how to determine the aspect of keeping Data local, as described below.
You could have certain pockets of personal data that can be transferred outside.
There could be certain pockets of data that could be transferred outside but a serving copy of the data has to be within the country
The third category is sensitive personal data ambit of sensitive personal data which has been widened considerably compared to what we saw under the 43A of IT ACT. For this, if sent out of
The fourth category is data that cannot be sent outside country at all.
“On Cross border transfer of data in addition to ‘consent’ there has to be standard contractual clauses (approved/prescribed by authority) or the transfer to a jurisdictions is approved by the central government”, he further explained.
What is the Data Protection Authority?
Supratim answered, “In the draft bill this seems to be all encompassing all powerful authority from rulemaking to advisory to enforcement. Therefore it is important to see how this really shapes up. In “IT Act”, section 43 A and 72A were largely there to cover the aspects of data privacy but enforcement and implementation.”
What are other important aspects to consider?
“There are many aspects but let us touch upon two given below”, said Supratim.
One is the requirement of having notices in multiple languages, which is not a very hard obligation the way it has been put. But in a country like India for say an e-commerce platform imaging the cost that one has to incur for putting multiple language notices. Also, we need to see are we able to really address the point of informed consent through this, because you also have a section of people who may be illiterates. Justice Srikrishna report suggest that we should have short videos or graphical representation which make it very easy for someone to understand the critical aspects of privacy.
Another important aspect is applicability of the law. This law is applicable to all processing that is happening in India and also to foreign bodies. Section 2(2) talks about applicability to foreign bodies, the first part says that “in connection with any business carried out in India”. This means a global platform that is accessible from India has to have the entire requirement of this law.
Are we going in direction of GDPR?
Supratim answered, “Whereas we are trying to follow the Gold standard and many countries are trying to follow the path set by GDPR, India is quite different country and we are not following everything the way it is in GDPR, we have to be mindful of our requirements. But the idea is slowly and surely reach a zone where we can have our laws quite akin to laws of matured jurisdictions.”
How does Bill address iSPIRT DEPA initiative?
Siddharth, sees this draft bill as a unique India first approach. He feels that apart from addressing privacy and data protection aspects it empowers Indians on having control on the use of their data for better financial services, better health services, education etc.
Siddharth goes on to explain that at iSPIRT for past 3-4 years we have been working at Consent layer of IndiaStack or Consent framework and it is great to see that bedrock of draft bill is actually based on consent and in that way it is somewhat similar to GDPR. But, one of the biggest problem they are facing in EU today is it is very difficult to operationalise consent. It is for the first time India has a unique infrastructure to operationalise consent.
“DEPA is nothing but a set of two tools that helps to operationalise consent, explains Siddharth.
One is known as Digital Locker system which allows to the federated exchange of data and second is known as electronic data consent, which is nothing but an electronic representation of user Consent.
“This means, if you want to share or allow your data from some provider to say another consumer, then you must be able to express what date you want to share with whom for what time period in some codified manner. This codified information or consent is known as consent artefact”, says Siddharth further.
As explained by Siddharth, the ‘consent artefact’ became a national standard in 2016 adopted by four financial sector regulator RBI, PFRDA, IRDA and SEBI and they adopted it for their entire eco-system.
Based on consent artefact every individual has an access to financial data and has a mechanism to share that data to gain access to a loan or any other services provider. This has been through an institutional mechanism called Account aggregator.
Siddharth further elaborated that, “the ‘Account aggregator’ (AA) is a class of entities known as data access fiduciaries. The AA unlike other parts of world decouples the institution that collecting consent from an institution that either consuming data or providing data. In EU e.g. as per of PSP2 directive the account information service provider which consumes data is also responsible for collecting the data.”
In India, 3 AA have been approved. Technical standard drafts are also out for ecosystem. And through AA you actually have an entity that’s working toward creating an informed consent experience. Going forward just like UPI you receive your consent for a payment, through AA you will have an entity that helps you provide and control consent. Based on Financial sector we have proposed a similar concept to TRAI for the telecom sector and health sector to NITI Ayog.
Has the AA concept been addressed in the bill?
Siddharth explains further, “The bill makes bedrock of most processing of data based on consent. AA model is nothing but your consent collector or Consent manager. Every data principle they have outlined right to confirmation and access, right to correction, most importantly the right to data portability. As a data principle from data fiduciary, you have the right to request and port machine structured non-reputable transaction history or any other user-generated data to other service providers. AA is nothing but a framework to operationalise this right.”
He further explained that in the report preceding the bill, they talk about a concept consent dashboard. AA is nothing but a consent dashboard. They had 2 tech innovation consent dashboard and data dashboard. You can log consent flows and data flows.
Will, there be consent dashboards concept like AA in other sectors also or will there be one single point authority under DPA?
Siddharth, “it would be a combination of both. If you see the draft bill, it allows sectoral regulators to write rules. For data the falls under private data sets category such as data pertaining to social media etc, DPA would prescribe an standard.”
The report talks about that dashboard can be maintained by each data fiduciary or it can be a common dashboard that everyone else agrees and follows. If you look at the account aggregator dashboard it is a common dashboard for the entire financial sector. But for social media companies can follow their won dashboards.
For any Software product companies that does not lie in any of the regulated sector can create their own consent dashboards, where the user can come see their dashboard correct their data, port the data, manage their consent.
Unlike the IT act, this regulation will have a direct bearing on any businesses processing data irrespective of being in a Software product or other domain. And hence there is a need to be attentive. How right is this aspect?
“Yes, the ambit increases quite a bit. Wherever there is sensitive personal data interface involved, the level of compliance requirement has gone up several times. In the IT Act, there was a mention of personal data in section 72A. The present draft bill does not talk about the deletion of 72A. The draft bill have a parallel mechanism set out in the IT Act”, mentioned Supratim.
Siddharth, “it is just not limited to compliance, this law unlocks the whole host of business models around data sharing around consented data sharing that you haven’t yet seen in any other country and it will be really interesting to space to see what companies get a build out there.”
Question from Participants.
What is the definition of data processing? Or what is the differentiation between Data Storage and Data Processing. E.g. if you are an email service provider, is it Data Storage or Data Processing? (asked by Chintan)
Supratim answered, “definition of data processing is extremely wide enough to make businesses fall in to ‘data processing category’ without being a processor.”
What is the timeline? (Asked by Chintan)
MeitY has asked for public comments by 10th of September on the draft bill, thereafter it will be presented to parliament and after promulgation, there will be more work in framing Authority, the rules by DPA etc. The law is not expected to be in implementable form only after 18 Months or so, minimum.
What happens to the Existing customer? Do we go back to them and get their consent? (Karthik)
Supratim answered, “whilst the it is not a retrospective legislation, if you continue processing without taking consent, you will fall foul of the requirement of law.”
Are there any fines defined here? (Karthik)
Yes, it has been taken care. Just like other aspects the draft bill he highly inspired by GDPR on this aspect also. We have 4% and 2% of annual turnover. There are 2 buckets 4% and 15 Cr and other is 2% and 5 Crore.
Do we need to appoint an DPO?
“There is a segregation which has been made of has significant Data Fiduciary under certain conditions will have to have DPO. Also, this law has an immense amount of significant rulemaking power, answered Supratim.
Hence, it will be seen in future how rules are framed by Authority. So, it has to be seen how business friendly the authority remains in rulemaking e.g. section 43A in IT ACT gave rule making power to define what is sensitive data and information and set out what is reasonable practices and procedure. In the rule made in future, we saw a plethora of requirements set out, over legislated and sometimes badly drafted.
The rules will go through an evolutionary cycle. Hence, the legislation has to be tested over a period of time as it unfolds, after crystallisation of this draft promulgation by parliament in to an ACT and rules being made after that on different aspects.
Disclaimer
PolicyHacks, and publications thereunder, are intended to provide a very basic understanding of legal/policy issues that impact Software Product Industry and the startups in the eco-system.
PolicyHacks, therefore, do not necessarily set out views of subject matter experts, and should under no circumstances be substituted for legal advice, which, of course, requires a detailed analysis of the relevant fact situation and applicable laws by experts in the subject matter on the case to case basis.
If you are facing an issue, we recommend you take expert professional advice on the case to case basis.
We intend to provide the best transcripts in the text part of the blog. However, it may not be an exact replica and maybe approximation, more standardised, normalised or moderated version of the expert view presented in the video.
The government of India had announced a Preferred Market Access (PMA) policy for Cyber Security products through an order notifying the Public Procurement (Preference to Make in India).
MeitY shall be the nodal Ministry to monitor and administer this PMA policy.
iSPIRT has been pursuing with MietY, application of PMA for all Indian Software Products to promote the Indian Software product industry and it is heartening to note that at least one important sub-sector of Cybersecurity has caught the Government’s attention.
iSPIRT organised a PolicyHacks session to understand this policy announcement with Ashish Tandon Founder & CEO of Indusface and Mohan Gandhi of Entersoftsecurity.
You can watch the discussion with Ashish and Mohan at below given YouTube video, in a question and answer format with Sudhir Singh.
What are the essential features of this Policy?
Ashish described the main features stating that this is a policy that is going to help boost Cybersecurity products in India. Govt. of India identified areas that require boosting ‘make in India’ products for the sensitive areas of cybersecurity.
Is there a way product companies can register or Government is going to keep a registry of ‘made in India’ products?
Ashish explains the policy has provided for the formation of a committee that will further provide for a process for empanelment of Indian Cybersecurity products and Indian Cybersecurity product companies with some defined key aspects that would qualify for empanelment.
Ashish further explained that as the empanelment aspects are decided there may also come up with a process for testing and meeting standards and quality norms etc.
Are there are enough product companies in ‘Cyber Security’ space for empanelment?
Mohan Gandhi answered that there are several product companies, but this policy should further strengthen the ‘make in India’ aspect and companies based out of India with deep tech product can look at getting this advantage of this policy.
Whether the Policy will be applicable to “productized services”?
Ashish answered, that this policy is applicable to the only product and at best give preference to made in India products in turnkey projects wherein a large project cybersecurity product is involved.
How will this policy help Start-up companies in Indian Market?
Mohan mentioned, that one interesting thing about this policy is that, it clearly talks about intellectual property. There is a need to register and prove that the IP belongs to India. It will encourage small companies to register the IP and leverage the Indian IP even when they are selling abroad.
Is there enough clarity exist on process and enplanement etc.?
Ashish feels the policy has already prescribed setting up of an empowered committee who will look at these aspects and it is MeitY that will be responsible for doing this.
Ashish further also elaborated that this Policy will get further push once some companies start getting empanelled and processes and rules are framed under MeitY by the empowered committee.
In concluding remarks, both Ashish and Mohan felt that Cybersecurity ecosystem will get a boost by this policy as the policy is furthering the cause by advising Government departments for preferring Indian products. With Digital economy on anvil, there should be a huge demand in Government and Public sector enterprises for cybersecurity. Cybersecurity product market is today dominated by players from the US, Europe and Israel.
The policy has to be pushed hard to further encourage and coupled with StartupIndia policy, there should be all-out effort to promote the Indian Cybersecurity product companies.
iSPIRT volunteers are strivers. We seek the good for our nation and our ecosystem. We brainstorm, ideate, experiment, build, and evangelize to fulfill our mission of making India a Product Nation. Every volunteer draws us into an ever-enlarging realm of intellectual possibilities and purposeful engagements.
Take Nikhil Kumar for instance. He stepped up almost two years ago to evangelize UPI and handhold its early adopters. He set out to create winning implementations that would put traditional payment systems to shame. Needless to say, this wasn’t an easy thing to do. There was no template to follow. And, most didn’t believe in the potential of this new breakthrough payment system. But this didn’t faze Nikhil. He had chosen his adventure inside iSPIRT and nothing could hold him back.
Today, UPI is a success story. However, that’s not the full story.
Nikhil showed us how to stay cool under fire, to foster affinity, and skillfully navigate diverse opinions amongst many stakeholders. His all-hands-on-deck work ethic came with an ability to take decisive action when the situation demanded it. He showed that a young volunteer can be a visionary with big plans and the capacity to bring them to life. He has set an example for all of us on how to pay-forward and serve a cause bigger than all of us. All this makes him an iSPIRT Volunteer Hero.
From tomorrow, Nikhil is shifting gears. He is stepping away from being a volunteer-in-residence. He is taking a few months break. After that, he plans to create a startup. This is great news for iSPIRT. While our India Stack and other technology public platforms create possibilities, it is the products and services that create value. We need all elements of a healthy society – sarkar, samaj, bazaar – to come together to solve population scale problems sustainably. So, we wish him all the very best in this new pursuit of excellence.
All shifts require an adjustment. While Nikhil will remain a part-time iSPIRT volunteer working on WANI, he will no longer be the iSPIRT voice on payments for media, policymakers, startups and financial institutions.
Nikhil’s lasting legacy is that he opened up iSPIRT volunteering for talented youngsters under-30s. Today we have more than a dozen young power volunteers. He has helped all of us see the particular gifts that these young volunteers bring to the cause. His spirit will live on!
By Sharad Sharma, Pramod Varma and Sanjay Khan Nagra for Volunteer Fellow Council
Since SaaSx second edition, I have never missed a single edition of SaaSx. The 5th edition – SaaSx was recently held on the 7th of July, and the learnings and experiences were much different from the previous three that I had attended.
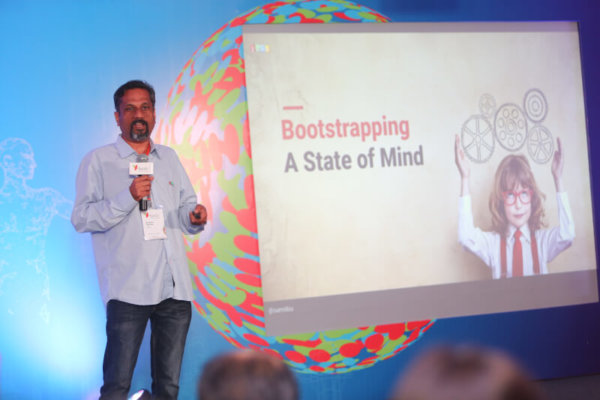
One primary topic this year was bootstrapping, and none other than Sridhar Vembu, the CEO and Founder of Zoho, was presenting. The session was extremely relevant and impactful, more so for us because we too are a bootstrapped organisation. Every two months of our 4.5 year-long bootstrapped journey, we have questioned ourselves on whether we have even got it right! If we should go ahead and raise funds. Sridhar’s session genuinely helped us know and understand our answers.
However, as I delved deeper, I realised that the bigger picture that Sridhar was making us aware of was the entrepreneurial journey of self-discovery. His session was an earnest attempt to promote deep thinking and self-reflection amongst all of us. He questioned basic assumptions and systematically dismantled the traditional notions around entrepreneurship. Using Zoho as an example, he showed how thinking from first principles helped them become successful as a global SaaS leader.
What is it that drives an entrepreneur? Is it the pursuit of materialistic goals or the passion to achieve a bigger purpose? The first step is to have this clarity in mind, as this can be critical in defining the direction your business would take. Through these questions, Sridhar showed that business decisions are not just driven by external factors but by internal as well.
For example, why should you chase high growth numbers? As per him, the first step to bootstrapping is survival. The top 5 goals for any startup should be Survive, Survive, Survive, Survive, Survive. Survival is enough. Keep your costs low and make sure all your bills are paid on time. Cut your burn rate to the lowest. Zoho created 3 lines of business. The current SaaS software is their 3rd. They created these lines during their journey of survival and making ends meet.
Why go after a hot segment (with immense competition) instead of a niche one? If it’s hot, avoid it i.e. if a market segment is hot or expected to be hot, it will be heavily funded. It will most likely be difficult to compete as a bootstrapped organisation and is henceforth avoidable. Zoho released Zoho docs in 2007, but soon as he realized that Google and Microsoft had entered the space, he reoriented the vision of Zoho to stay focused on business productivity applications. Zoho docs continues to add value to Zoho One, but the prime focus is on Applications from HR, Finance, Support, Sales & Marketing and Project Management. Bootstrapping works best if you find a niche, but not so small that it hardly exists. You will hardly have cut throat competition in the niche market and will be able to compete even without heavy funding.
Most SaaS companies raise funds for customer acquisition. Even as a bootstrapped company customer acquisition is important. As you don’t have the money, you will need to optimise your marketing spend. Try and find a cheaper channel first and use these as your primary channel of acquisition. Once you have revenue from the these channels, you can start investing in the more expensive one. By this time you will also have data on your life time value and will be able to take better decisions.
Similarly, why base yourself out of a tier 1 city instead of tier 2 cities (with talent abound)? You don’t need to be in a Bangalore, Pune, or a Mumbai to build a successful product. According to Sridhar, if he wanted to start again, he would go to a smaller city like Raipur. Being in an expensive location will ends up burning your ‘meager monies’ faster. This doesn’t mean that being in the top IT cities of India is bad for your business, but if your team is located in one of the smaller cities, do not worry. You can still make it your competitive advantage.
Self-discipline is of utmost importance for a bootstrapped company. In fact, to bootstrap successfully, you need to ensure self-discipline in spends, team management, customer follow-ups, etc. While bootstrapping can demand frugality and self-discipline, the supply of money from your VC has the potential to destroy the most staunchly disciplined entrepreneurs as well. Watch out!
And last but not the least – It takes time to build something successful. It took Zoho 20 years to make it look like an overnight success.
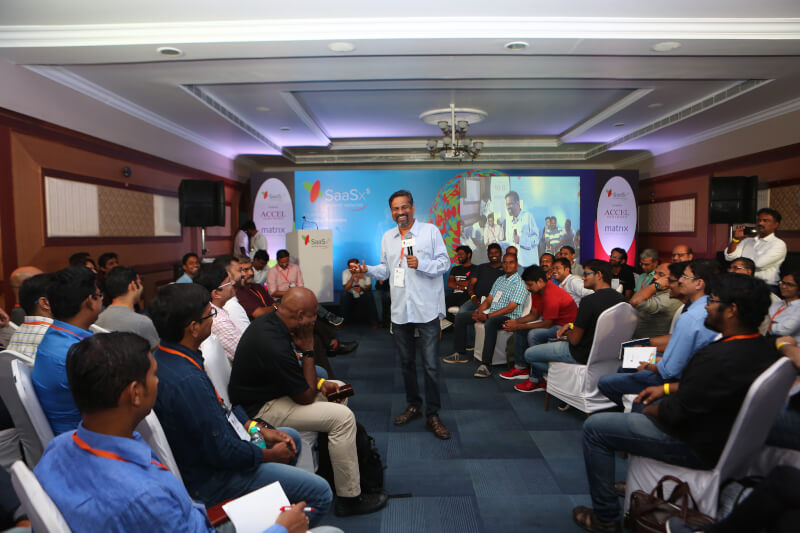
As a first time attendee of iSPIRT‘s annual SaaSx conference, I didn’t know what to expect as we drove along the western coast of India towards Mahabalipuram – the venue for SaaSx5. From all the chatter around the event on Twitter, it looked like the who’s who of SaaS leaders in India were attending. Upon arrival, I took my seat with my colleague and looked around. There were only about 100 people in the room, very different from most conferences I’d attended in the past – a lot more exclusive, and a melting pot of SaaS founders building a diverse set of products. It had all the markings of an inspiring day, and it did not disappoint.
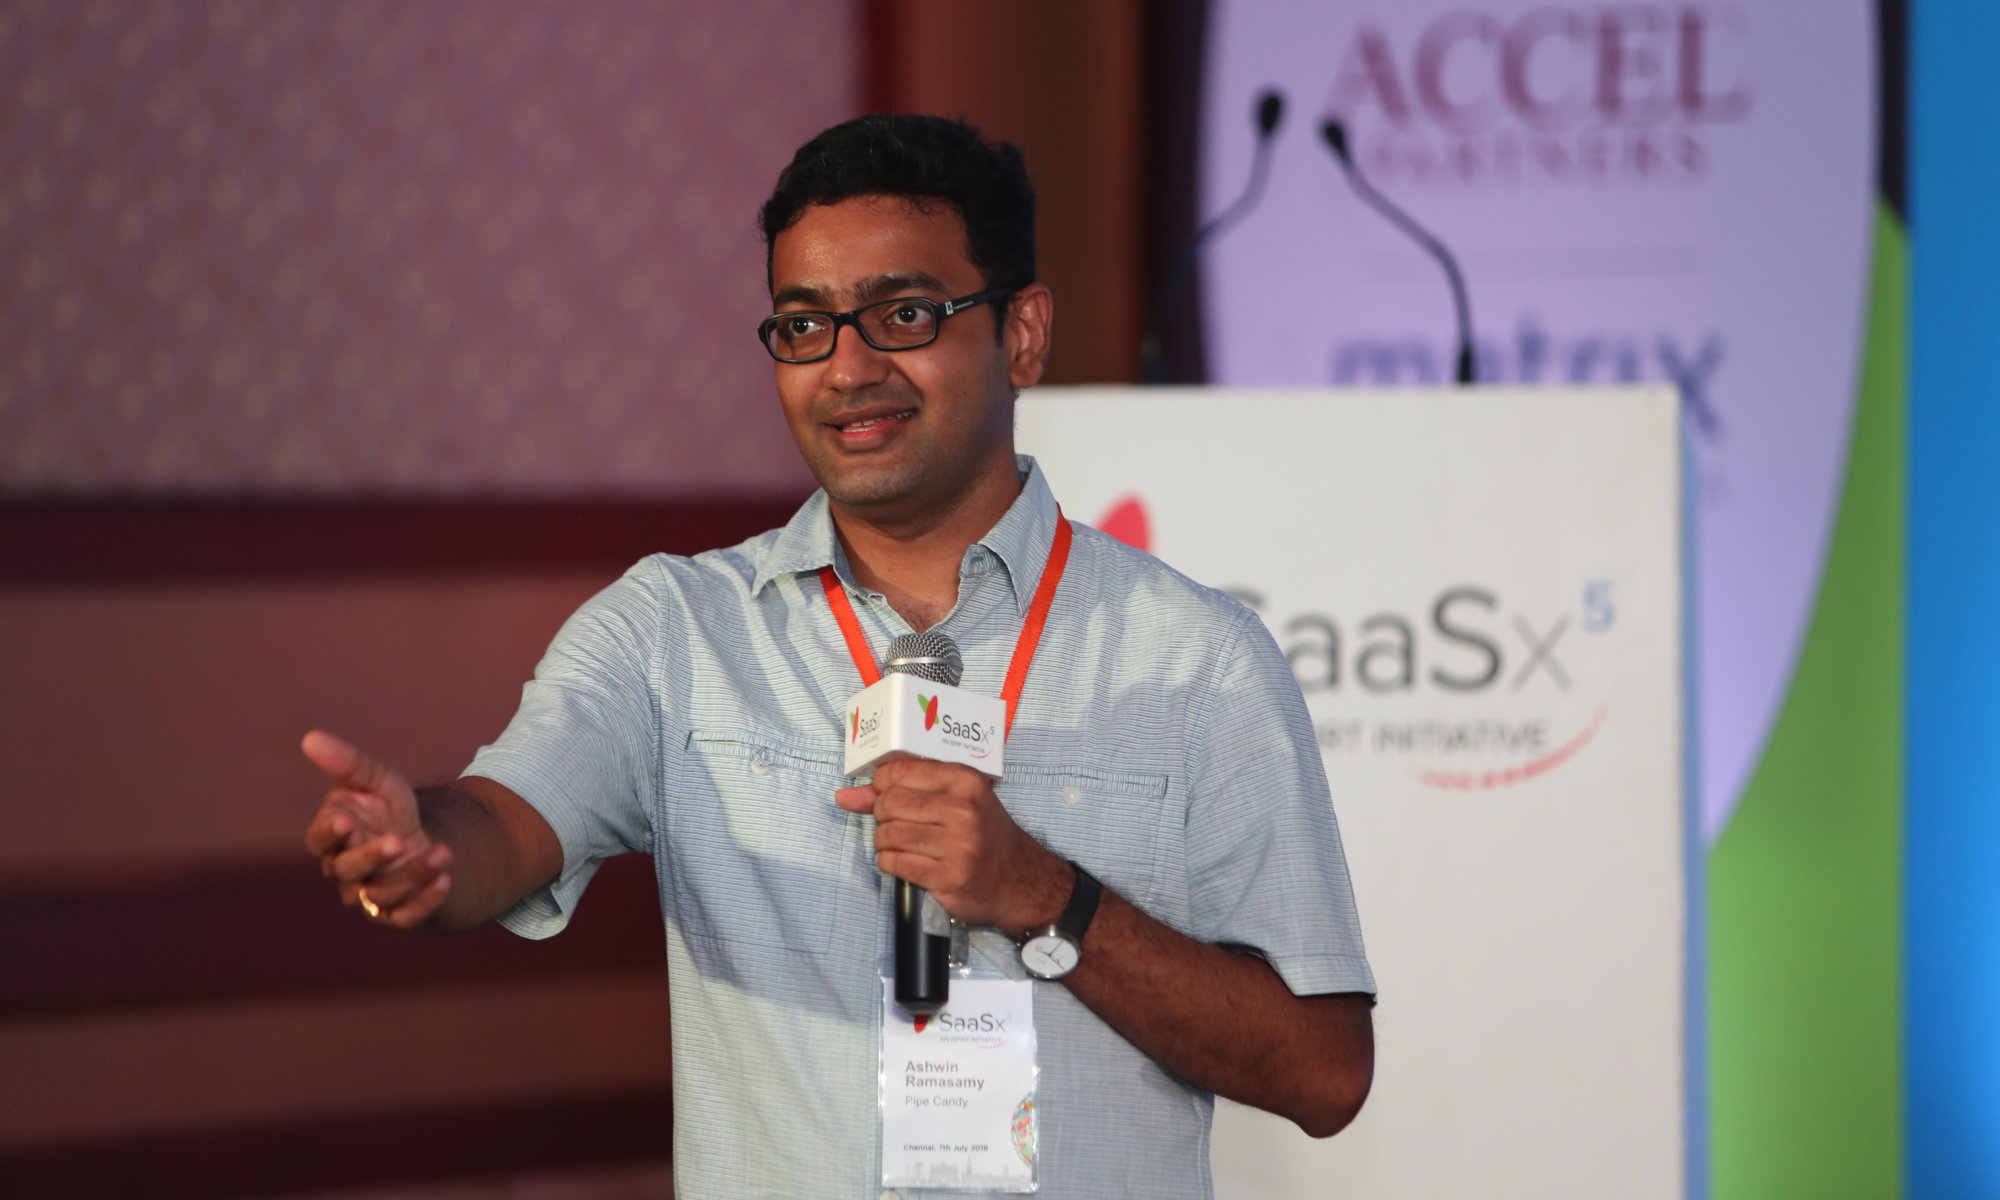
Starting with a keynote from the estimable founder of Zoho, Sridhar Vembu, the day was packed with talks and discussions focused on growing one’s SaaS company in the current technology landscape, primarily led by founders of notable SaaS companies of the country. One such event was an unconference on “Setting up and Scaling Sales across Segments and Geographies”, led by Ashwin Ramasamy from PipeCandy.
Picture this: about 80 founders seated in a room, circled around Ashwin who was leading the conversation about setting up and scaling your sales team. Since the flat organizational hierarchy at SignEasy, and the culture of openness at the company provide me with a wonderful vantage point of all functions across our company, including sales, I was eager to listen to the different perspectives that the founders brought to the table. At the start of the discussion, Ashwin graciously asked the audience for talking points they’d like covered, and the discussion began. A plethora of topics were discussed, starting from the very definition of inside sales, leading up to when and why to deploy an inside-sales team. Hiring and putting together the right sales team, including whether it should be in-house or outsourced, was another hot topic of debate with many founders offering their own experiences and perceptions.
The conversation then steered towards outbound sales and the mechanics and economics of that, which contributed to some of the biggest takeaways for me – things that cannot be found in a book and are only learned through experience.
The success rate of outbound sales peaks at 2%, as opposed to the 40-50% success rate you come to expect with inbound sales. This was an interesting insight, as it’s easy to assume your outbound effort is underperforming when it could actually be doing quite well. Also, you should use the interest you’re receiving through the inbound channel to refine your outbound strategy – your inbound interests are a goldmine of information on the kind of industries, company sizes, and job functions your potential customers represent. At SignEasy, we are constantly honing our outbound target by capturing as much information as possible from our inbound requests.
Further, the efficacy of your outbound sales effort is a direct function of the maturity of the market you’re in – for a saturated market with tens of other competitors, outbound usually fails to make a mark because it’s difficult to grab a potential customer’s attention. This is a great rule of thumb to decide if outbound is for you, depending on the market your product serves.
Outbound sales also requires dedicated effort rather than a ‘spray and pray approach’ – a minimum 6-month commitment is crucial to the success of your outbound strategy. Founders should be deeply involved in this initial effort, sending out 500 emails a day for at least 3 months, and tweaking and iterating through them as they get to the most effective email. It’s also important to dedicate yourself to a channel when experimenting, but also experiment and exhaust numerous channels over time to zero in on the most effective ones.
The value of this discussion, and indeed the day, was best expressed by the ferocity with which my colleague and I took notes and wrote down every piece of advice that was being dropped around the room. Being product leads of the SMB business and mobile products respectively, Phalgun and I were amazed at how much we could relate to each point being discussed, having been through and living the journey first-hand ourselves at SignEasy.
SaaSx5 was nothing short of inspiring, and we emerged from it feeling uber-optimistic about SaaS in India, and what the future holds
2 days to go for #SaaSx5 and we are reaching our limits for this year. I had missed a few folks in the first batch of 50 announced, so including them along with the next 20+ (in no particular order).
For people who are have attended earlier SaaSx I don’t need to tell this, but for all those who are attending the event for the first time – SaaSx is an informal event for knowledge sharing by SaaSprenuers for SaaSprenuers. This is why we have it on the beach for the last 3 years. 🙂
If you don’t know what this is about, SaaSx5, iSPIRT Foundation flagship event for software entrepreneurs of India, is being held in Chennai on 7, July 2018 (Saturday). SaaSx has been instrumental in shaping Global Software from India in the last 3 years. This year the theme is to help SaaS entrepreneurs setup for growth over the next 1-2 years.
So the first 50 confirmed list #SaaSx5 companies is here. It has been a slog for us going through all the applications we received, especially the initial drive to set extremely fair criteria and process. Listening to feedback from earlier SaaSx this year we decided to allow Founder and +1 (from their leadership team). Having a tag team we believe is extremely helpful to the founders in learning, assimilating and taking it back to their teams. This also meant that given the small limited space we had to be strict in our curation to ensure most SaaS product startups had an opportunity.
By the time this post goes live many other invites will have been sent and confirmed. We will continue to announce the companies finalized as we go along, so they can start preparing for the amazing sessions.
There are still spots, so if you have not registered or confirmed your invite (check your email), please do it quickly.
In no particular order, here are the first 50 (based on their confirmations).
Thanks to our many behind the scenes volunteers who have been tirelessly working on getting us this far and continuing on. Thanks to Chirantan & team from Software Suggest for crafting this post.