Every day, businesses in India spend countless hours navigating multiple government portals, repeatedly submitting the same information and managing fragmented compliance processes—not because regulations require it, but because government systems do not work together.
For years, reforms have focused on improving the Ease of Doing Business (EoDB) by simplifying regulations and reducing procedural burden. While these efforts remain important, the next leap requires a different mindset—an Alternate Way of Doing Business (AWDB), where businesses no longer act as the integration layer between disconnected government systems. AWDB is about redesigning the digital experience of regulation—not changing the regulations themselves.
India’s businesses face a double compliance challenge
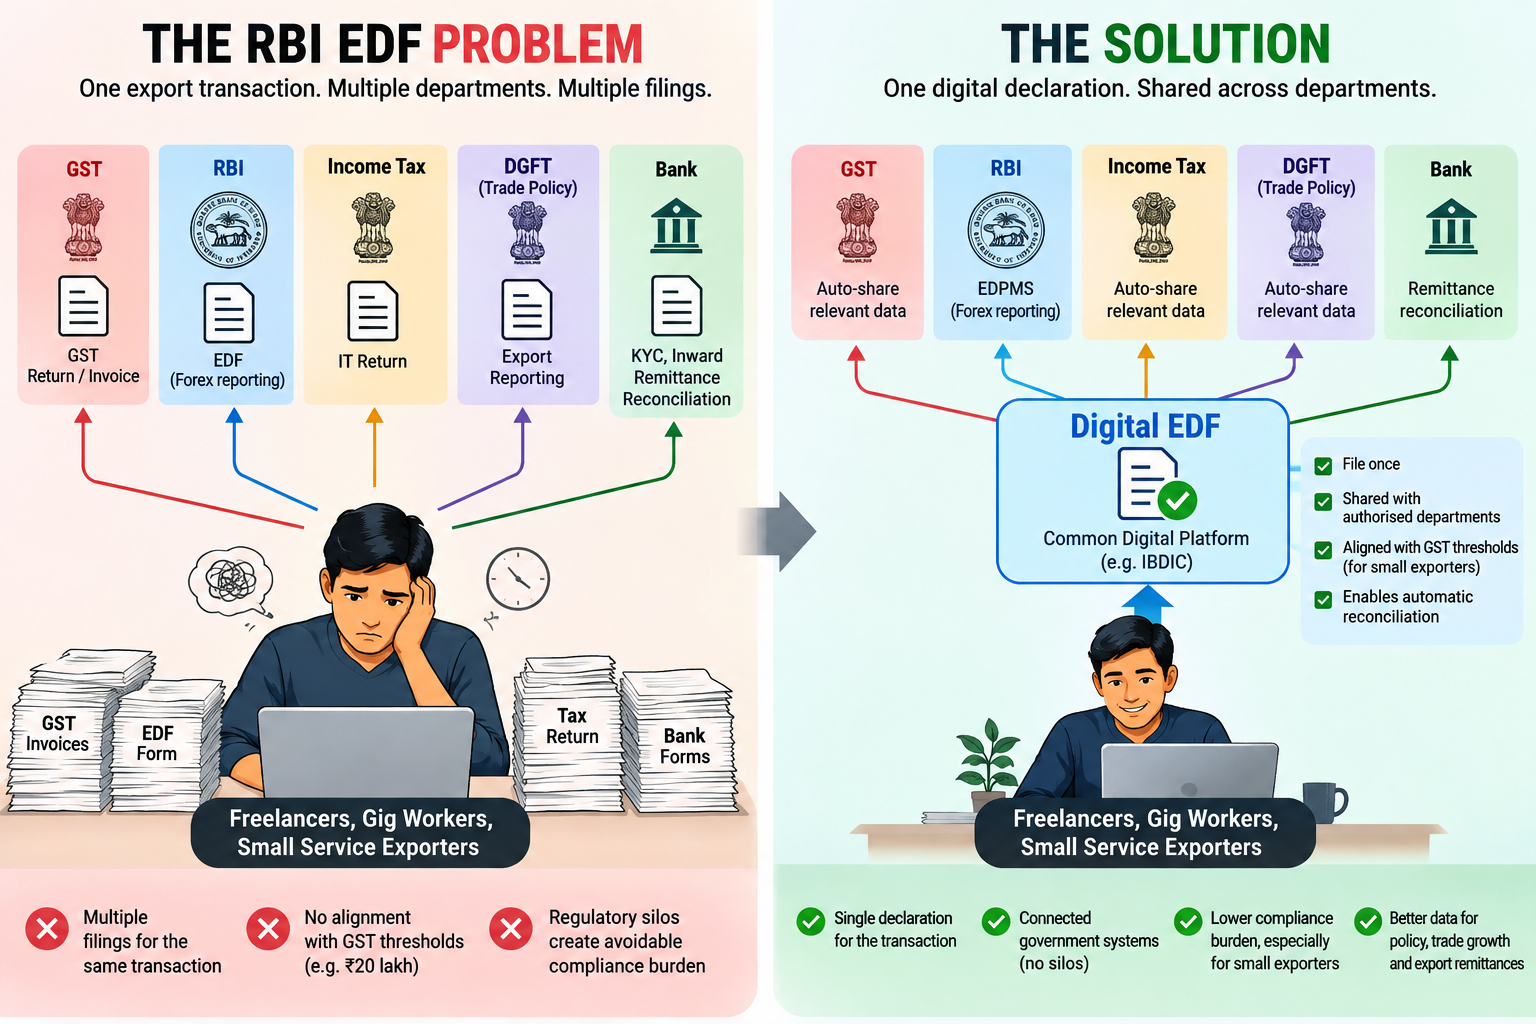
Every business in India—whether a startup, MSME, manufacturer, exporter, hospital or large enterprise—operates within a complex regulatory landscape. As they grow, they interact with a wide range of regulators, including GSTN, MCA, EPFO, ESIC, FSSAI, RBI, DGFT, Pollution Control Boards, labour departments, municipal bodies and numerous state authorities. Each regulator serves an important public purpose, yet the overall landscape is difficult to navigate. Businesses often struggle to determine which regulations apply to them, when obligations arise, and how requirements vary across sectors, jurisdictions and stages of their lifecycle. This information asymmetry is the first layer of friction. The second layer begins once these obligations are understood. The regulatory ecosystem largely functions as a collection of independent digital silos, each with its own portal, identifiers, workflows and data requirements. Businesses repeatedly submit the same information, upload identical documents, undergo multiple verifications and manage separate compliance journeys for different regulators. Systems that should exchange information seamlessly instead rely on businesses to bridge the gaps between them.
Regulatory Cholesterol: The hidden friction that arises when regulatory systems operate in silos, requiring businesses to repeatedly bridge information gaps and duplicate compliance efforts.
The result is invisible friction that slows businesses without improving regulatory outcomes. Time and effort are spent navigating disconnected systems rather than meeting substantive compliance obligations. This unnecessary overhead created by fragmented regulatory systems rather than regulation itself is what we call regulatory cholesterol.. Removing it is not just about reducing regulation; it is also about making regulation discoverable, interoperable and significantly easier to comply with.
The DPI Playbook: Connect Systems, Not Interfaces
India’s Digital Public Infrastructure (DPI) journey has demonstrated that systemic inefficiencies are best addressed through shared digital infrastructure rather than isolated digitisation of departments. UPI did not replace banks, it connected them through common protocols. DigiLocker did not replace document issuers, it enabled trusted exchange of verifiable digital documents. API Setu did not replace government systems, it provided a common interface for secure data exchange.
The success of these platforms stems from a common design philosophy: preserve institutional autonomy while enabling interoperability through shared standards, protocols and trust frameworks. The next frontier is to apply the same design philosophy to India’s regulatory ecosystem—connecting regulators rather than consolidating them. This is the vision behind the proposed National Regulatory Compliance Grid (NRCG).
Single Window Access Is Only the Beginning
Over the past few years, initiatives such as the National Single Window System (NSWS) have made it easier for businesses to discover approvals and access government services through a common interface. This is an important step towards reducing information asymmetry. However, a single entry point does not, by itself, make the underlying regulatory ecosystem interconnected. Behind the window, businesses still encounter multiple systems, each with its own data model, identifiers, workflows, evidence requirements and integration mechanisms.
The real challenge is structural. Every regulator continues to evolve independently, resulting in bespoke integrations, duplicated data exchanges and fragmented compliance journeys. Each new integration adds to the ecosystem’s technical debt, while businesses remain responsible for repeatedly providing the same information across agencies. Governments incur the cost of maintaining overlapping digital infrastructure, and technology providers build and maintain countless point-to-point integrations. The problem is therefore not one of access alone—it is fundamentally one of interoperability.
From Fragmented Systems to Connected Regulatory Systems
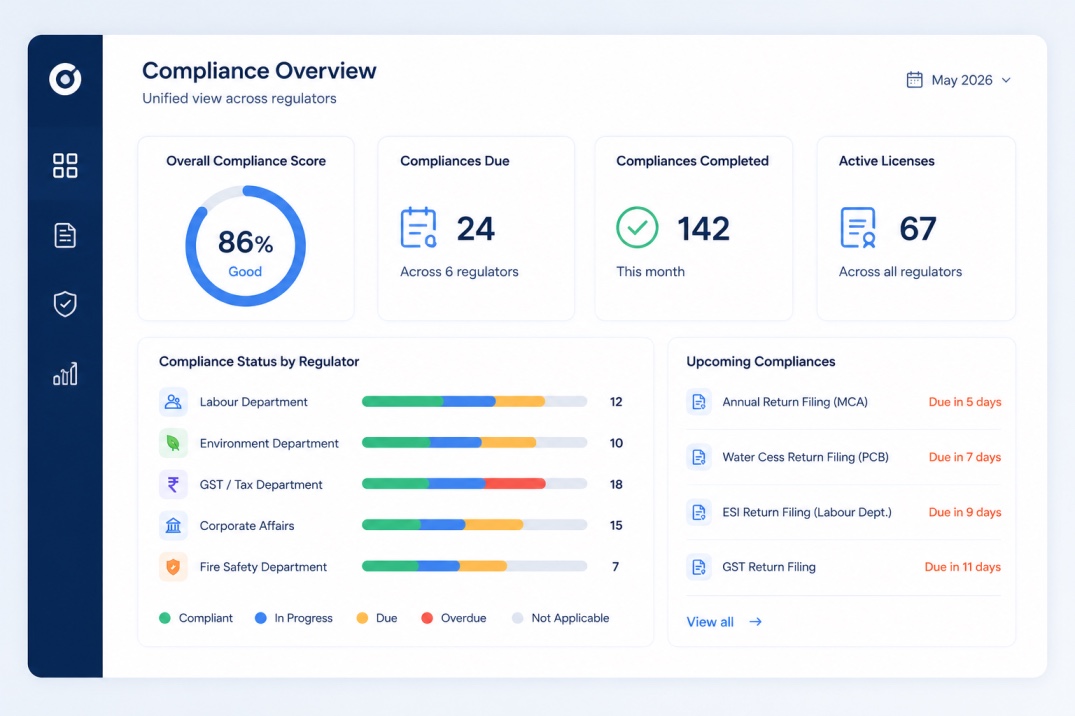
Imagine a regulatory ecosystem where regulators continue to operate independently, but their digital systems speak a common language. Instead of functioning as isolated digital silos, regulatory platforms are connected through common standards and shared digital building blocks. An enterprise establishes its identity once and can be recognised consistently across regulatory interactions. Digital credentials become reusable, compliance evidence becomes machine-verifiable, and common regulatory services can be leveraged across agencies.
This does not require replacing existing regulatory systems or centralising regulatory data. Each regulator continues to own its legislation, business rules, applications, databases and approval processes, while adopting common digital infrastructure where collaboration and connectivity create value. The result is a federated regulatory ecosystem—autonomous regulators connected through shared digital rails.
This is the design philosophy behind the National Regulatory Compliance Grid (NRCG). NRCG is not another government portal or a centralised compliance application. It is a Digital Public Infrastructure (DPI) for regulation—a lightweight connectivity layer that provides common standards, shared digital building blocks and reusable public services, enabling independent regulatory systems to work together. Just as UPI enables seamless payments across independent banks without replacing their core banking systems, NRCG enables seamless compliance across independent regulators without centralising regulatory functions or data. It provides the connective fabric that allows businesses, regulators and service providers to participate in a trusted regulatory ecosystem.
The architecture of NRCG is Guided by five design principles:
- Choice of access: Businesses should be able to interact with regulatory services through the channel of their choice—government portals, private compliance platforms, ERP systems, APIs or AI agents. Compliance should be accessible wherever businesses already work, rather than requiring every interaction to occur through a single government application.
- Reuse of common digital capabilities: Regulators should be able to leverage shared digital building blocks—such as enterprise identity, authorisation, registrations, filings, payments, certificates and notifications—instead of independently developing similar capabilities. Reusable public digital infrastructure reduces duplication, improves consistency and accelerates digital transformation across government.
- Shared trust infrastructure: Trusted regulatory interactions require common foundations. Shared enterprise identity, delegated authorisation, harmonised identifiers, verifiable digital credentials and reusable compliance evidence should establish trust across regulatory boundaries, enabling information to be accepted once and reused wherever appropriate.
- Standards-based connectivity: Independent regulatory systems should interoperate through common metadata standards, canonical data models, open APIs and machine-verifiable evidence. Rather than relying on bespoke point-to-point integrations, systems should speak a common digital language that enables secure, seamless and scalable information exchange
- Federated by design: NRCG should strengthen—not replace—existing regulatory institutions. Each regulator continues to own its legislation, policies, business rules, applications and data while participating in a common digital ecosystem through shared standards, trusted services and interoperable digital infrastructure. The objective is connected systems, not centralised systems.
Towards Frictionless Regulatory Infrastructure
Ease of Doing Business is often viewed as a policy challenge. Increasingly, it is becoming a systems challenge. When regulatory systems cannot communicate with each other, businesses become the integration layer. They repeatedly submit the same information, upload documents across multiple portals, prove their identity to different agencies, reconcile conflicting records and navigate fragmented workflows that often ask essentially the same questions in different ways.
Technology should eliminate this burden—not merely automate existing processes. NRCG shifts compliance from document exchange to trusted data exchange; from manual verification to machine-verifiable evidence; and from fragmented regulatory workflows to coordinated digital journeys. The objective is not fewer regulations. The objective is frictionless regulation. The impact of NRCG extends beyond improving government efficiency. An interoperable regulatory infrastructure creates the foundation for a broader innovation ecosystem. Software providers can build compliance platforms without integrating separately with every regulator. AI assistants can help enterprises understand and fulfil regulatory obligations across agencies. Professional service firms can deliver end-to-end digital compliance solutions. Industry bodies can create sector-specific applications, and startups can innovate on standard APIs rather than reverse-engineering government systems.
This is the same pattern that has emerged across India’s Digital Public Infrastructure journey. Shared infrastructure such as identity, payments, document exchange and consent layers have enabled new forms of innovation by allowing public and private actors to build on common digital rails. Regulatory interoperability represents the next evolution of this journey. The vision is not one regulator, one database or one portal. It is one connected regulatory network—where regulators retain their autonomy while participating in a trusted digital ecosystem; where compliance becomes predictable, programmable and increasingly invisible; and where businesses spend less time navigating systems and more time creating value, generating employment and driving economic growth. Removing regulatory friction is not about reducing regulation. It is about enabling government systems to work together as one. That is the promise of the National Regulatory Compliance Grid (NRCG).